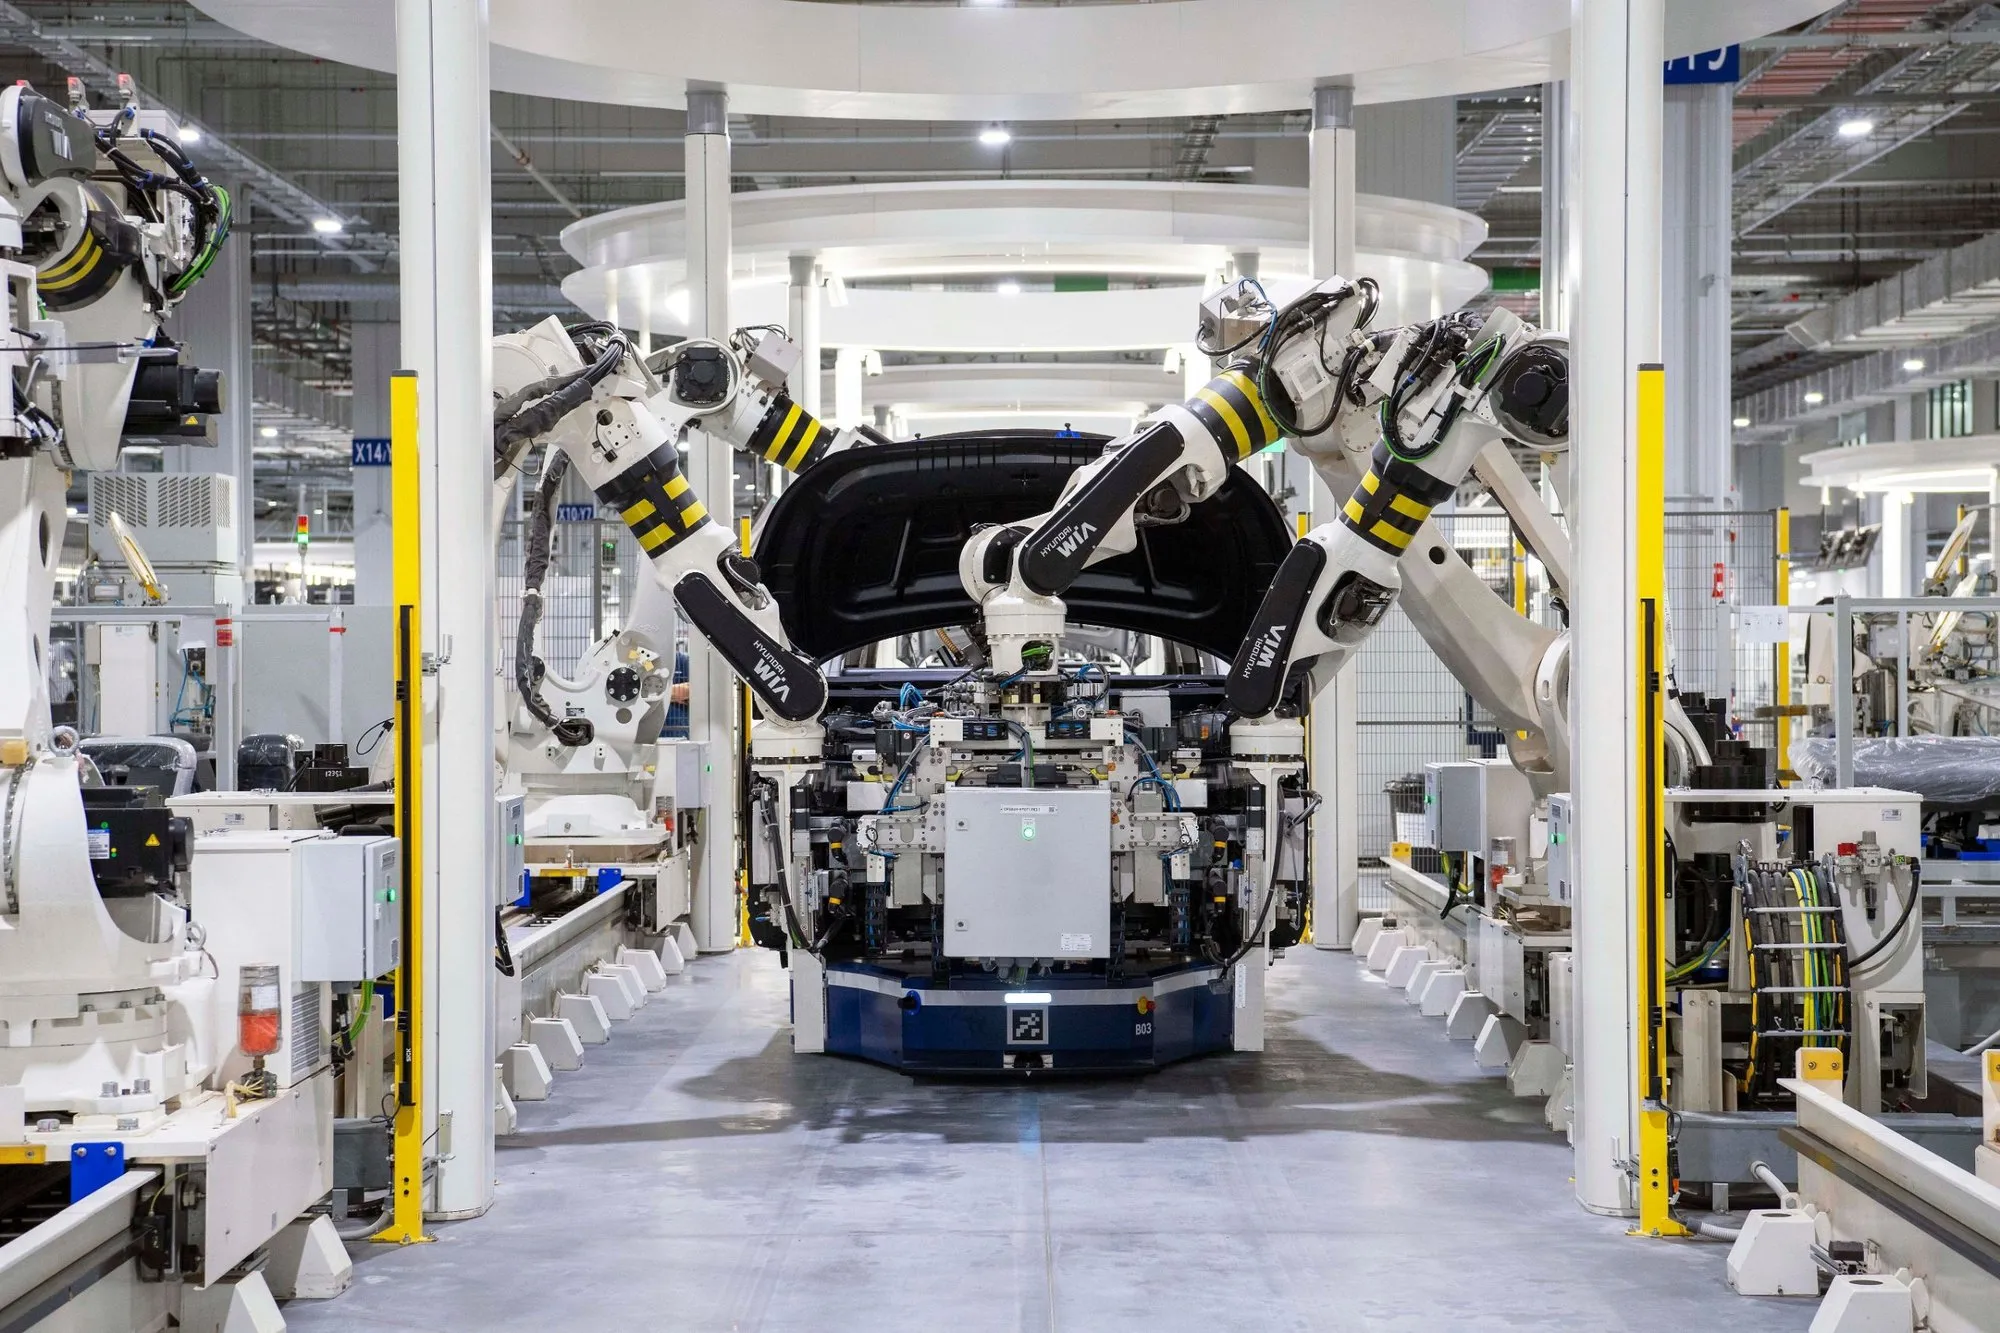
Operational technology (OT) runs the physical world: plant, pumps, building systems, ships and trains. It has its own demands for performance, reliability and safety. The US National Institute of Standards and Technology (NIST) has published a draft update of its main guide to securing it.
NIST guidance is voluntary for most organisations, and this is a draft. There is nothing to comply with yet. Anyone who runs OT, or depends on suppliers who do, can comment until 30 November 2026.
What’s changing
NIST published the initial public draft of SP 800-82 Revision 4, “Guide to Operational Technology (OT) Security”, on 21 September 2026. It was written by authors from NIST and MITRE. It covers typical OT system designs, common threats and weaknesses, and recommended security measures.
NIST lists these changes in the revision:
- More sectors. Coverage now includes building automation, water and wastewater, food and agriculture, freight rail and maritime vessels. It also covers industrial Internet of Things systems that connect to the cloud.
- Built around CSF 2.0. The guide is restructured around the NIST Cybersecurity Framework (CSF) 2.0. Risk management material now sits under the Govern function.
- OT risk in enterprise risk. It discusses how OT risk management fits into enterprise risk management, referring to NIST IR 8286r1.
- The Risk Management Framework. A new appendix covers applying the NIST Risk Management Framework to OT.
- More on controls. Guidance on asset management, and on network monitoring and detection, is expanded.
- Architecture. It adds guidance on protecting system management functions and applying zero trust principles.
Comments are due by 30 November 2026. The draft, a comment template and submission details are on NIST’s publication page.
What it means for you
The draft treats OT risk as part of enterprise risk, governed through the CSF 2.0 Govern function. A sensible way to use it:
- Read the draft while it’s open. If something won’t work for your sector, use NIST’s comment template before 30 November.
- Know what you run. List your OT systems and connected devices, with owners and where they sit.
- Bring OT risk into the main register. Make sure the board sees OT risks alongside the rest, in terms it can weigh.
- Include suppliers. Integrators, equipment makers and cloud services often hold access to OT. Record them and what they can reach.
- Check you can see trouble. Ask whether your monitoring would spot unusual activity on OT networks.
- Map to CSF 2.0. If you already use CSF 2.0, the revised guide will fit more easily.
How RiskWitness helps
Record your OT assets. Add each system with an owner and where it’s kept or hosted. Link it to its risks, controls and suppliers.
Record each risk with an owner. Score likelihood and impact before and after controls. Add a cost range, so the board sees the risk in financial terms. Set a review date.
Show the controls. Link controls such as asset inventory, monitoring and network separation to each risk. Record how effective each is and test it. Map controls to the requirements of the built-in RiskWitness Blueprint, such as RW-DEV-01 (a list of every device) and RW-NET-10 (network divided into zones).
Work to CSF 2.0 as well. On Team and above, you can add NIST CSF 2.0, or any framework you’re licensed to use, as one of your own. Paste its requirements in from your own copy. One control can meet requirements in several frameworks at once.
Cover your suppliers. Record integrators and equipment makers with their criticality. Keep their questionnaires, assurance evidence and contract clauses.
Make the decision visible. Record a treatment for each risk: reduce, transfer, avoid or accept. An acceptance needs a reason and an expiry. Outside tolerance, a named approver signs it off and confirms it’s them.
Give gaps an owner. Turn each one into an action with a due date. Overdue actions show on the dashboard.
Take it to the board. Produce a PDF report or slide deck. Record the committee meeting, its minutes and its decisions.
Every step is kept in a history that shows who did what, when, and the old and new values. Nobody can edit or delete it. When the board, an auditor, a customer or a regulator asks how OT risk is managed, the answer is already written down.
Sources
- Guide to Operational Technology (OT) Security: NIST Requests Comments on Draft SP 800-82r4, NIST, 21 September 2026
- News: draft guide to OT security, NIST Computer Security Resource Center, 21 September 2026
- SP 800-82 Rev. 4 (Initial Public Draft), NIST Computer Security Resource Center, 21 September 2026