Your information security risks, controls, frameworks and policies, in one place.
RiskWitness holds your information security risks, the controls that reduce them and every decision made about them, in a history that can only be added to. When your leadership, an auditor or a customer asks, the answer is already there.
- Reports for your leadershipPDF reports and slide decks from the register
- Two-step sign-inFor everyone, with passkeys and SSO
- Free for everyone elseOwners, approvers and viewers cost nothing
- Any framework you work toThe RiskWitness Blueprint built in, plus ISO 27001, NIST CSF and more
Every decision is witnessed.
For every risk, control and acceptance, RiskWitness records who decided what, when, and on what evidence. That history can only be added to: the app can't edit or delete it, and the database underneath refuses to.
Who decided
Every change carries the name of the person who made it, and accepting a risk asks them to confirm it's really them.
What changed
Old and new values are kept side by side, so you can see exactly how a score, owner or decision moved, and when.
On what evidence
Control tests, files and comments are linked to the risk, so the reasons for a decision stay with it.
From a list of worries to a register you can defend.
The steps every risk goes through, each one recorded.
Identify
Start from a library of common risks picked for your sector and size, or import the spreadsheet you have.
Score
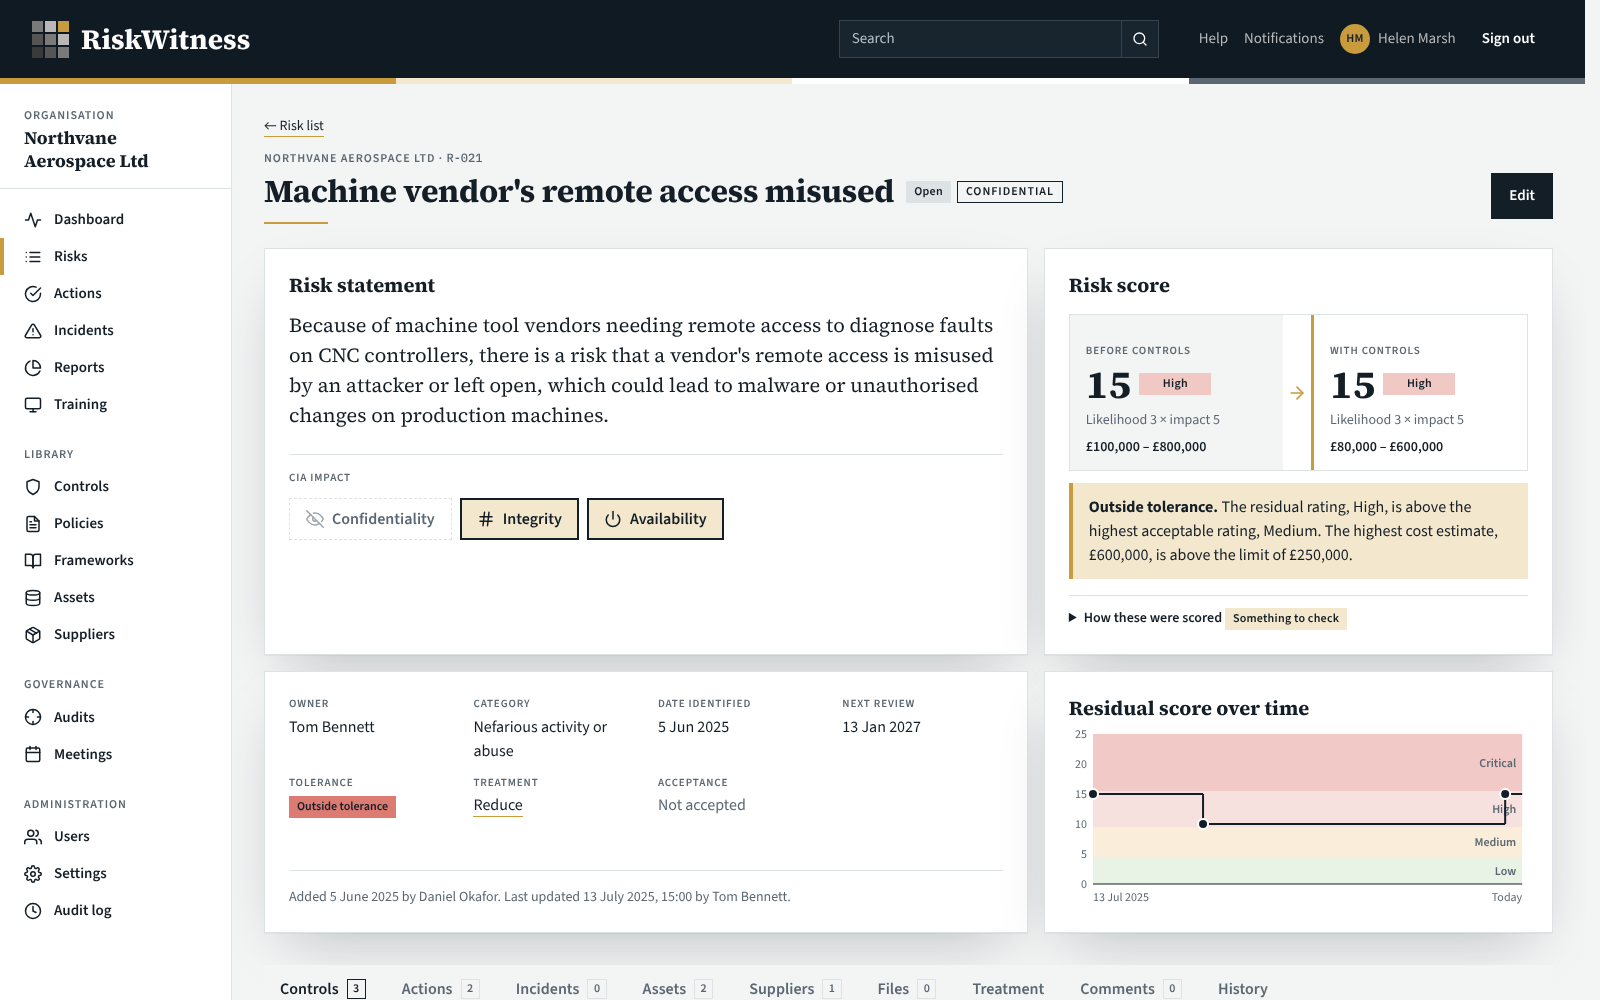
Likelihood and impact on your own scale, before and after controls, with a cost range if you want one.
Control
Link the controls that reduce each risk, give them owners, and record how they test.
Decide
Reduce, transfer, avoid or accept. Acceptances outside tolerance go to a named approver.
Review
Review dates by rating, reminders to owners, and a trend over time for your leadership.
New to risk registers? Read our guide: The information security risk register: what goes in it, and how to keep it useful
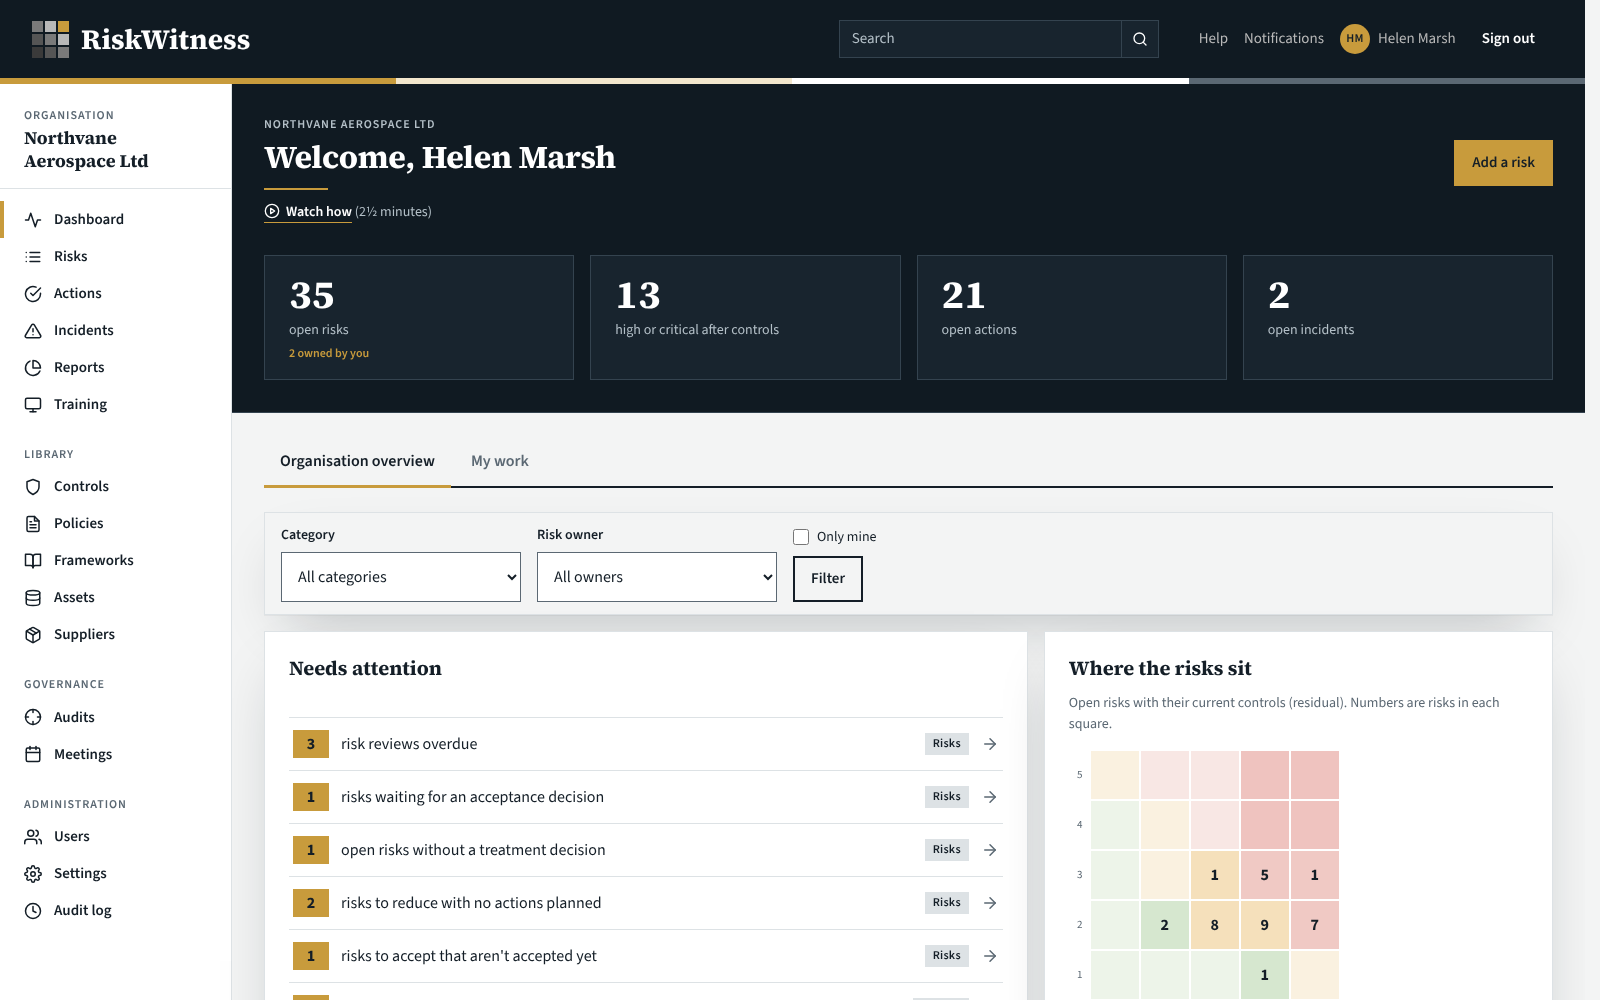
Your whole register, on one screen.
What needs attention today, what's overdue, and how each risk has moved, for everyone from risk owners to the board.
Everything around your risks, in the same place.
Controls and testing
Each control has an owner, an effectiveness rating per risk, and a record of every test and its result.
Frameworks
See which requirements your controls and policies meet, and where the gaps are, framework by framework.
Actions
The work to improve, assigned with due dates, on a board or a list, linked to the risks it reduces.
Incidents and regulators
Record incidents, who handles them, and the regulators you may need to tell, with their deadlines.
Suppliers
Criticality, assurance evidence, contract clauses and reviews for the third parties you depend on.
Policy packs
Your information security policies, written from the Blueprint for you to tailor, approve and keep joined up to your controls.
Work to any framework you're licensed for.
Start with our free RiskWitness Blueprint, built in. Then bring the others you answer to, map the controls you already have, and see the gaps against each one.
- The RiskWitness BlueprintBuilt in, free, with starter controls already mapped
- Other frameworks, such as ISO/IEC 27001 and NIST CSFWhere you have a licensed copy
- Industry standards and regulationsWhatever your licence or the law gives you
- Your customers' requirements, or your own internal standard
One control can meet requirements in every framework at once, so work you do once counts everywhere. Starter has the Blueprint's Foundation tier, Team and above all three. Your own frameworks are a bolt-on on Team, and included from Business. Framework names belong to their owners; RiskWitness isn't affiliated with or endorsed by them, and you add their content from your own copy.
Built the way you'd expect a security product to be.
Your risk register describes your weaknesses. It deserves better care than most places it's kept.
- Two-step sign-in for everyone
- Authenticator apps, passkeys or security keys, or your own single sign-on. There's no way to switch it off.
- A history nobody can rewrite
- The audit trail can only be added to, enforced by the database itself, not just the application.
- Backups we test
- Encrypted nightly copies kept away from the live service, and one restored every week to prove it works.
- Each customer kept apart
- Every page checks which organisation you belong to, and automated tests try to cross between customers on every change.
See it with your own risks.
Try it free for 30 days in a register of your own. No card needed. Plans start at £1,950 a year (excluding VAT), and everyone beyond the people who run the register joins free.